A Fake Claude Code Extension Tried to Open a Backdoor to Your PC
Real Python AI News · Weekly edition · The week of October 31–November 6, 2026
Stop Falling Behind on AI. Catch Up in Five Minutes.
New models, new prices, new agent tools, all the time. Our new AI newsletter gives you the handful of stories you actually need as a developer. Free, straight from the Real Python team.
This week’s news is about trust in AI tools: a coding add-on that hides a trap, a model built to find security holes, and new ways to tell where AI-written text comes from. Here’s each story in plain language.
A Booby-Trapped Claude Code Extension Slips a Backdoor Onto Programmers’ Computers
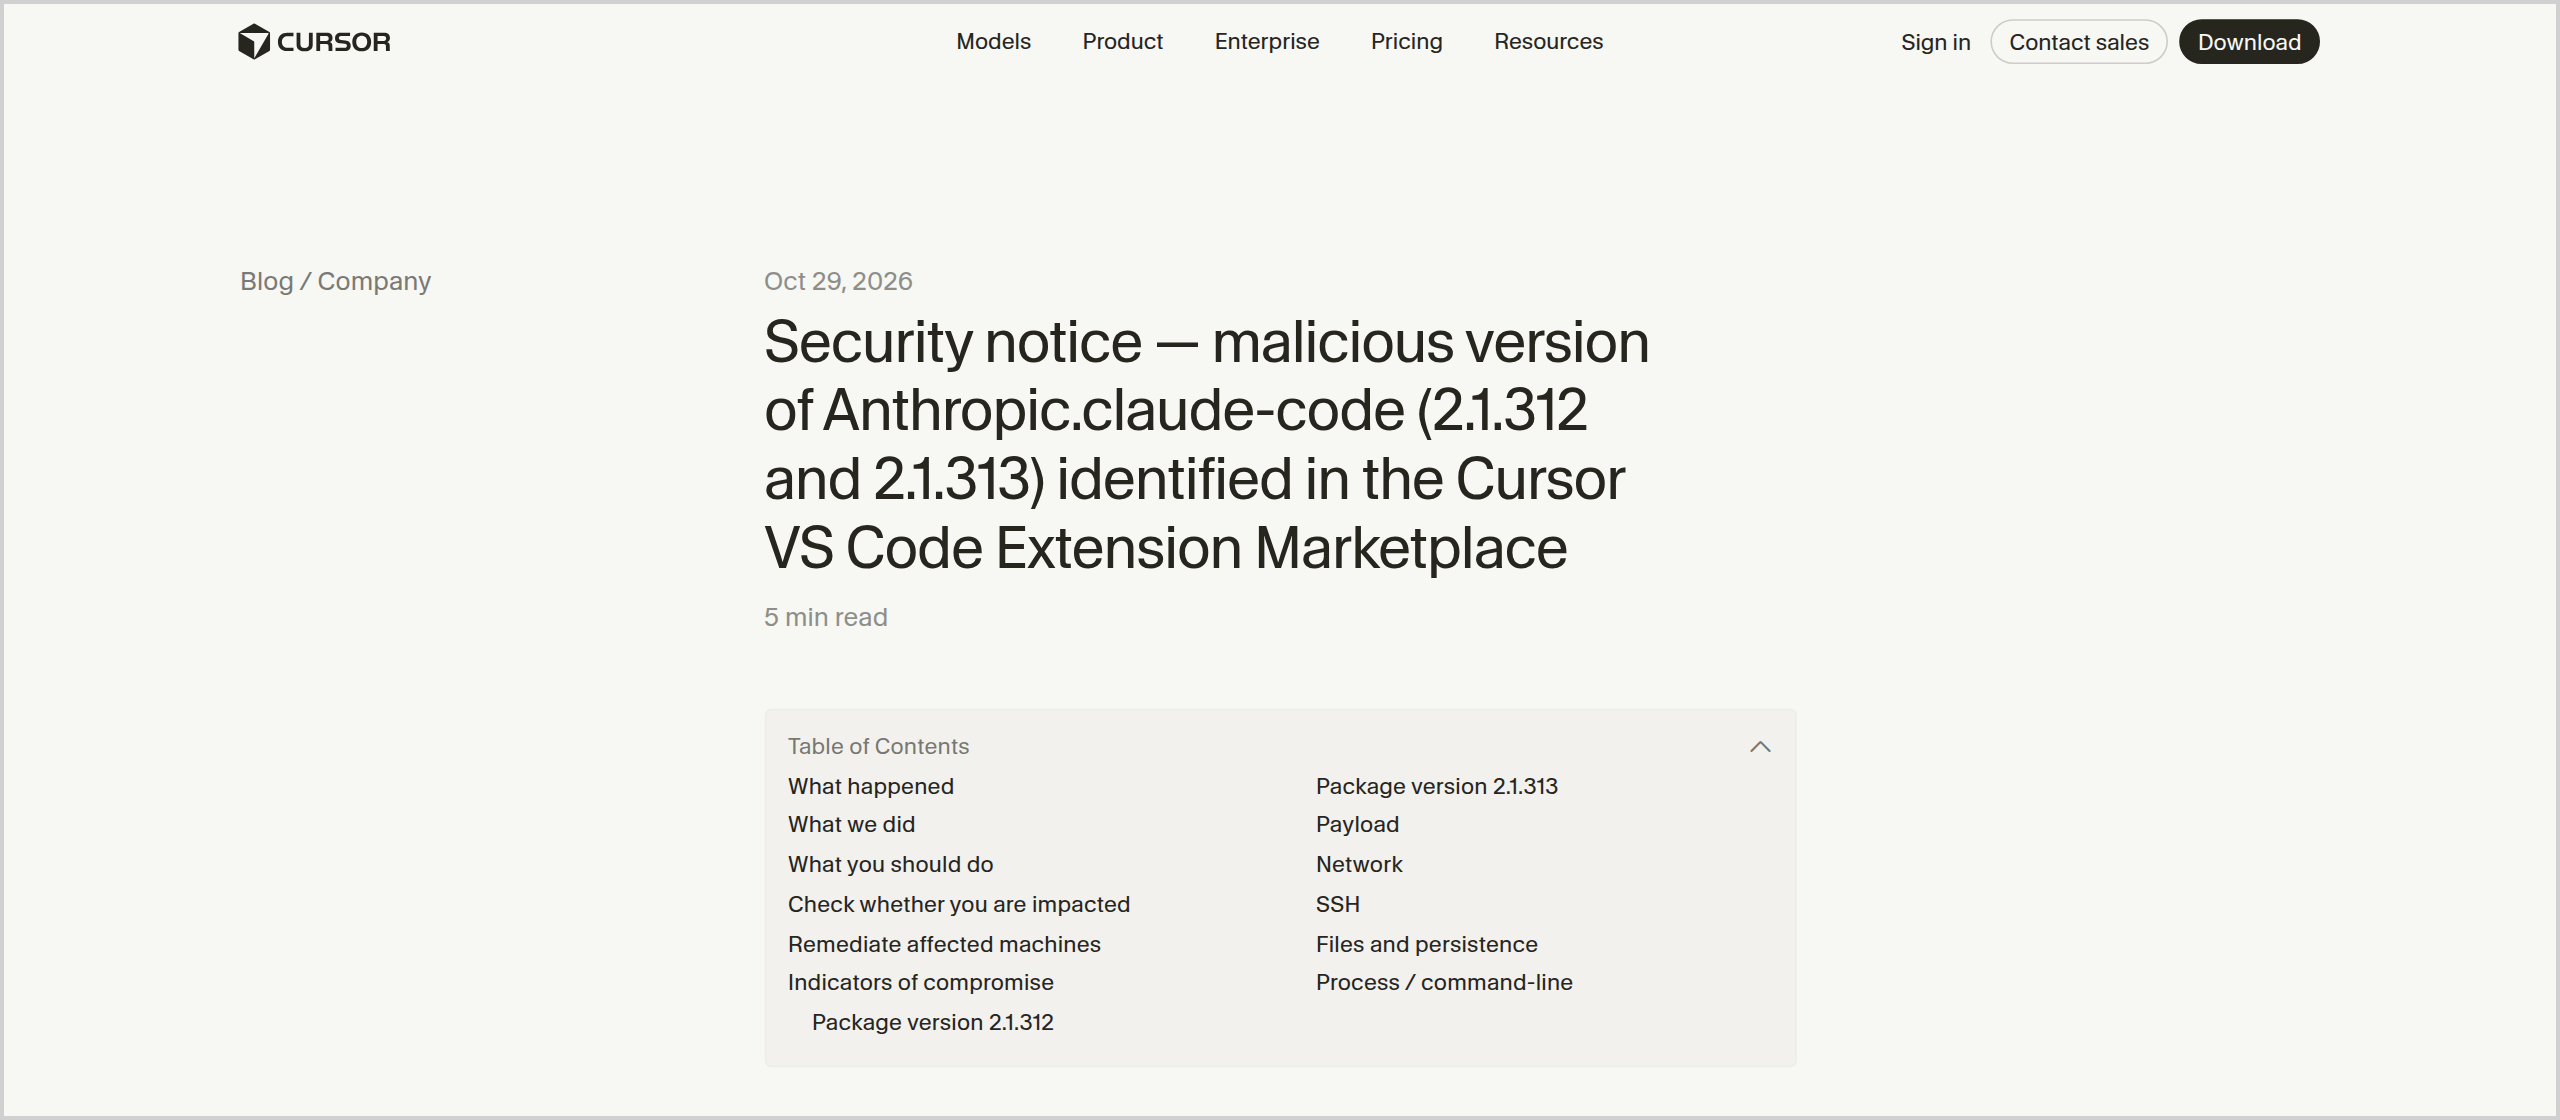
A trusted name in an app store for programmers turns out to hide a backdoor. The store belongs to Cursor, an app for writing code.
Cursor’s security notice says two versions of the extension for Claude Code, Anthropic’s AI coding assistant, are tampered copies Anthropic didn’t build: 2.1.312 and 2.1.313. They were up for about 11 hours on October 29 and target Windows PCs and Macs.
The fake extension goes after SSH, a standard way to log in to a computer from afar. An SSH key works like a pass that needs no password. The extension adds the attacker’s key, labeled svc-telemetry, to the computer’s approved keys, starts automatically when the computer restarts, and reports details like the username. Cursor says switching SSH on requires administrator rights, so on most machines that step fails.
Cursor pulled both versions and got the attacker’s server shut down. Researchers at OpenSourceMalware say the copies from npm (a public library of code), Open VSX, and Microsoft’s store are clean. Cursor users should check their version and look in their SSH settings for a svc-telemetry key. Since uninstalling may not be enough, Cursor offers cleanup scripts.
“Attackers like extension stores because one poisoned upload reaches everyone who trusts the name on it. AI coding assistants make a tempting disguise, since they run right next to company code and passwords. Businesses whose staff code in Cursor now have a version number, time window, and key name to check.”
— Philipp Acsany, Real Python
OpenAI’s Security AI Hunts Down Software Flaws, but Only Vetted Experts Can Use It
GPT-6 Cyber, OpenAI’s new AI model for security research, hunts for vulnerabilities, weaknesses in software that attackers could abuse. It then proves each flaw is real by writing an exploit, working attack code that triggers it.
OpenAI says its researchers used the model to build exploits for 948 flaws in Linux, the software behind most of the world’s servers, and sent 304 critical findings to Linux’s maintainers with suggested fixes. It also credits the model with finding 81 unknown high-severity bugs in Firefox, many already fixed.
Irregular, an independent testing company, sees a more mixed picture: the model cleared all 11 scenarios in one test set but solved 90 of 288 challenges in another, slightly fewer than OpenAI’s general-purpose GPT-6 Astra.
Read the full article at https://realpython.com/ai-news-weekly-2026-11-06/ »
[ Improve Your Python With 🐍 Python Tricks 💌 – Get a short & sweet Python Trick delivered to your inbox every couple of days. >> Click here to learn more and see examples ]